Check Point bypassed ChatGPT Lockdown Mode to leak full chat histories through a popup
Check Point Research said on 5 November 2026 that a popup flaw in ChatGPT's HTML preview defeated Lockdown Mode and leaked chats. OpenAI fixed it in September.
By Emre A.Published
 Tech AI Latest
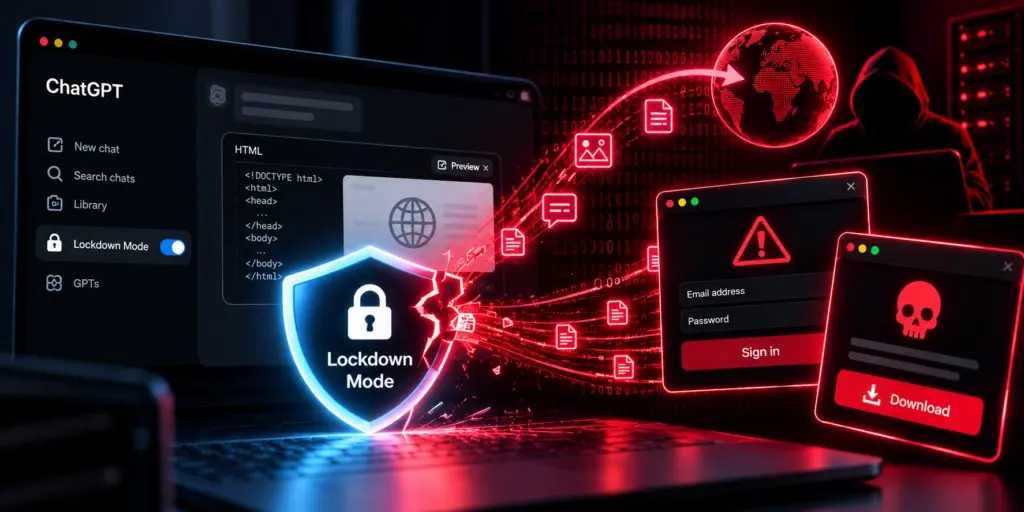
Check Point Research disclosed on 5 November 2026 a way around ChatGPT Lockdown Mode, the setting OpenAI built to stop prompt injection from sending data out of a chat. A nested frame in the HTML preview for code blocks could open a popup outside the sandbox and send the whole chat history to an attacker. In the ChatGPT Classic desktop app no click was needed. OpenAI fixed the flaw on 18 September 2026.
Key facts
- Disclosed: 5 November 2026 by Check Point Research
- Root cause: the HTML preview iframe kept the allow-popups and allow-popups-to-escape-sandbox permissions
- Impact: silent theft of chat history and uploaded files, fake sign-in windows, malware disguised as updates
- Worst case: the Electron-based ChatGPT Classic desktop app, where popups opened with no user action
- Fixed: 18 September 2026, by removing both popup permissions; no user action needed
- Not stated: a CVE number, a bounty amount or an OpenAI statement
What Check Point found
Check Point Research published a report on 5 November 2026 titled ChatGPT Lockdown Mode Bypass: Phishing, Malware Delivery, and Silent Data Exfiltration. It describes a way to defeat Lockdown Mode in ChatGPT, the optional setting that OpenAI introduced to stop a hijacked conversation from sending data to an outside server.
The flaw sat in the HTML preview that OpenAI added to ChatGPT code blocks in February 2026. The preview renders HTML inside nested sandboxed iframes. According to Check Point, the outer frame kept two permissions, allow-popups and allow-popups-to-escape-sandbox. OpenAI's own script replaced the browser's window.open function so that new windows needed approval, but that override only covered the top-level page. A nested frame could call its own copy of the function, open a popup that was no longer sandboxed and run arbitrary HTML there, outside the network limits that Lockdown Mode enforces.
How an attack would work
Check Point says an attack could start in three ways: a crafted prompt, a malicious custom GPT or a shared chat. In one demonstration, a malicious GPT quietly sent the messages of the conversation to a server the researchers controlled. The same technique could send the full chat history and uploaded files, show a fake sign-in window to collect credentials, or deliver malware presented as a legitimate update, the researchers say.
The browser version needed a click from the user in most scenarios, according to coverage of the report. The ChatGPT Classic desktop app, which is built on Electron, was the more dangerous surface: there window.open worked without any user gesture, so simply chatting with a malicious GPT was enough to leak the conversation. Check Point describes that case as zero-click.
Why this matters for Lockdown Mode users
OpenAI introduced Lockdown Mode on 13 February 2026 together with new risk labels for connected features. The setting does not try to stop injected instructions from reaching the model. Instead it removes the tools an attacker would use for the last step, sending data out: browsing is limited to cached content and features such as Deep Research and agent mode are restricted. It launched for Enterprise, Edu, Healthcare and Teachers plans and later reached more account types.
That design makes the exfiltration channel the whole defence, and the Check Point report shows that a rendering feature outside the model could reopen that channel. The people most likely to switch Lockdown Mode on, such as security teams and organisations handling sensitive data, were the ones relying on that guarantee. Check Point also argues in a company blog post that the case shows a wider problem: AI assistants keep adding interface features, and each one can widen what an injected prompt can reach.
It is the second report in two weeks that runs through the same HTML preview. On 28 October Parameter disclosed a shared-link account takeover in ChatGPT that also started from code rendered in the preview sandbox.
The fix and what to watch
OpenAI fixed the issue on 18 September 2026 by removing both popup permissions from the outer HTML preview iframe, according to Check Point, which says it retested afterwards and confirmed the technique no longer works. The fix was made on OpenAI's side, so users do not need to update anything. ChatGPT Classic continues to receive security patches. The roughly seven weeks between the fix and publication follow the usual practice of disclosing only after a patch is live.
Check Point's report does not give a CVE number, and OpenAI has not published its own statement or said whether it paid a bounty. For shared chats from unknown senders, coverage of the report recommends opening them in a private browser window without signing in. The open question is how many other interface features, from previews to canvases and connectors, sit outside the controls that Lockdown Mode was designed to enforce. More AI security disclosures are collected in our cybersecurity coverage.
What changed
| Before | Lockdown Mode was presented as blocking the data exfiltration step of prompt injection attacks in ChatGPT |
|---|---|
| After | Check Point showed the HTML preview could open an unsandboxed popup that bypassed those limits; OpenAI removed the popup permissions on 18 September 2026 |
| Who it affects | ChatGPT users with Lockdown Mode enabled, especially on the ChatGPT Classic desktop app; organisations relying on it for sensitive data |
Questions people ask
- Is ChatGPT Lockdown Mode still vulnerable?
- No. Check Point says OpenAI removed the two popup permissions on 18 September 2026 and its retest confirmed the technique no longer works.
- Do users need to do anything?
- No update is needed because the fix was made on OpenAI's side. Lockdown Mode remains available and can stay switched on.
- What data could an attacker take?
- Check Point says the bypass could send the full chat history and uploaded files to an attacker, and could also show fake sign-in windows or deliver malware posing as an update.
Sources
- ChatGPT Lockdown Mode Bypass: Phishing, Malware Delivery, and Silent Data Exfiltration (Check Point Research, 5 Nov 2026)
- ChatGPT Lockdown Mode bypass reveals a wider challenge in AI security (Check Point, 5 Nov 2026)
- Introducing Lockdown Mode and Elevated Risk labels in ChatGPT (OpenAI, 13 Feb 2026)
Reference pages
- Check Point Software Technologies company
- OpenAI company
- ChatGPT tool
Spotted an error? See the corrections policy and tell the editor. Facts in this story come from the sources listed above; vendor claims are attributed.
Comments
Loading comments.